
Daybreak says I'm all set. Codex still blocks my own security audit.
I asked ChatGPT Codex to check dependencies and close known security holes in my own codebase and servers. Codex had already helped build and maintain this system. Then the audit chat repeatedly failed with a cybersecurity error.
I told it that I was already in Daybreak Blue. I told it that the code and servers were mine. The same error kept appearing.
This is a record of that experience on November 9, 2026, with evidence and the gaps kept visible.
Evidence note: All four screenshots were recaptured as lossless browser PNGs on November 9, 2026. Each file retains at least two image pixels per CSS pixel at its published width. They were not enlarged or converted from JPEG. Crops and pixelated redactions are labeled below; the originals are retained privately. The failure record was read through the app's chat tools.
The codebase is mine
The toolkit behind Namegarage has a private GitHub repository under my
account. The commit history
repeatedly shows nikolay and codex authored. The repository owner remains
visible in the breadcrumb above the history.
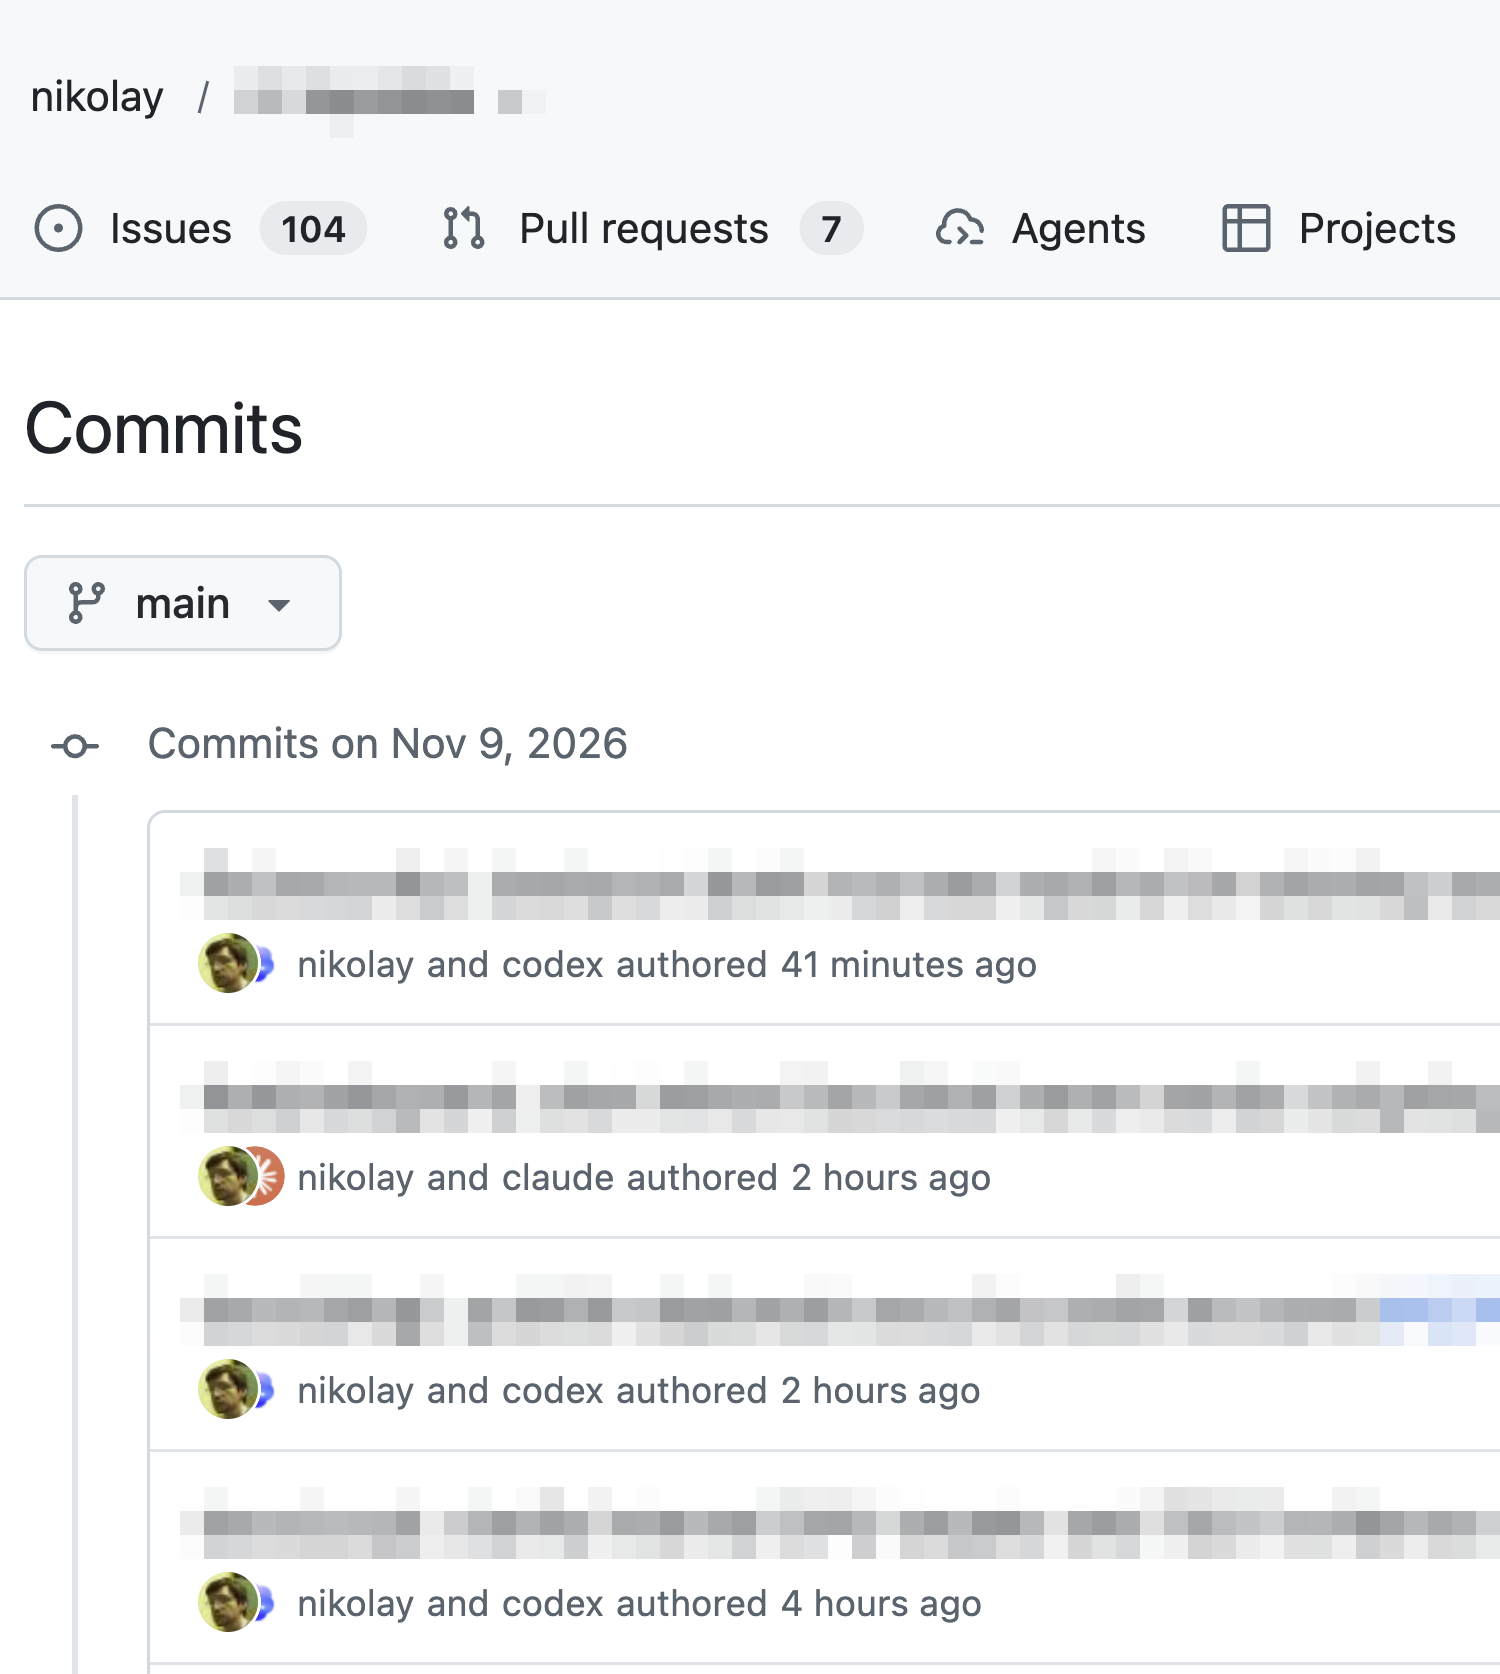
Cropped browser capture from November 9, 2026, taken after the recorded failures. Three visible entries credit nikolay and codex; one credits nikolay and claude. The repository owner, dates and author credits remain visible. The repository name and commit messages have pixelated redactions; commit hashes are not shown. The breadcrumb identifies the repository owner; the three Codex entries record its participation.
Open full-size PNG (1500 × 1674; new tab)The servers are mine, too
The audit concerns the OVHcloud VPS services that I control for Namegarage. The repository contains their infrastructure configuration, maintenance tools and verification records. These are the systems I asked Codex to secure.
The authenticated OVHcloud console identifies the account as Nikolay Kolev. Its VPS inventory lists two Namegarage services, both Active. The review image pixelates the provider hostnames and datacenter locations.
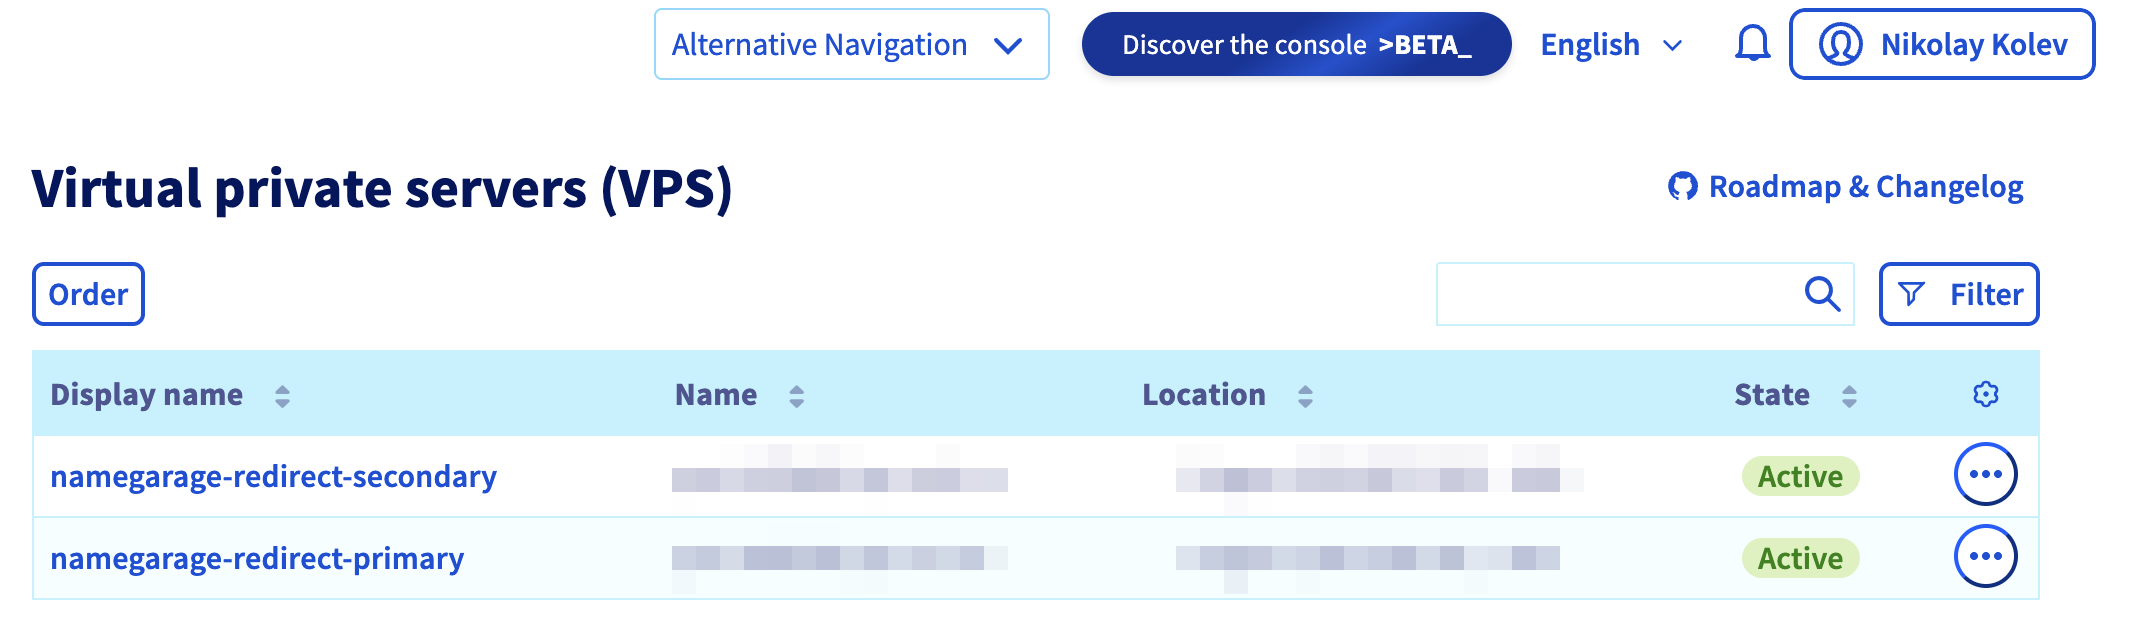
Cropped browser capture from November 9, 2026. Pixelated redactions cover provider hostnames and locations. The account name, branded service labels and Active states remain visible. The original is retained privately.
Open full-size PNG (2136 × 620; new tab)The maintenance history also records work on these servers. The cropped
pull-request header below shows a security update opened under my account
and merged from a codex/ branch. The commit history above separately
records Codex's author credits. The audit chat reports completed package
maintenance on both hosts before the later failures.

Cropped browser capture of the merged server maintenance change. Its title,
author, Merged badge and codex/ branch remain visible. The PR description,
package versions, CVE details and rollout procedures are outside the crop.
This was ongoing maintenance of an existing system, with a recorded history of the owner's instructions and Codex's work.
I am already in Daybreak Blue
I reported my enrollment repeatedly in the audit chat. To document it, I asked Codex to inspect the browser's Daybreak account page.
The page says “You're all set” and “You've completed all required steps.” It checks off Advanced Account Security, identity verification and Daybreak keys. It also offers a Go to Codex button.
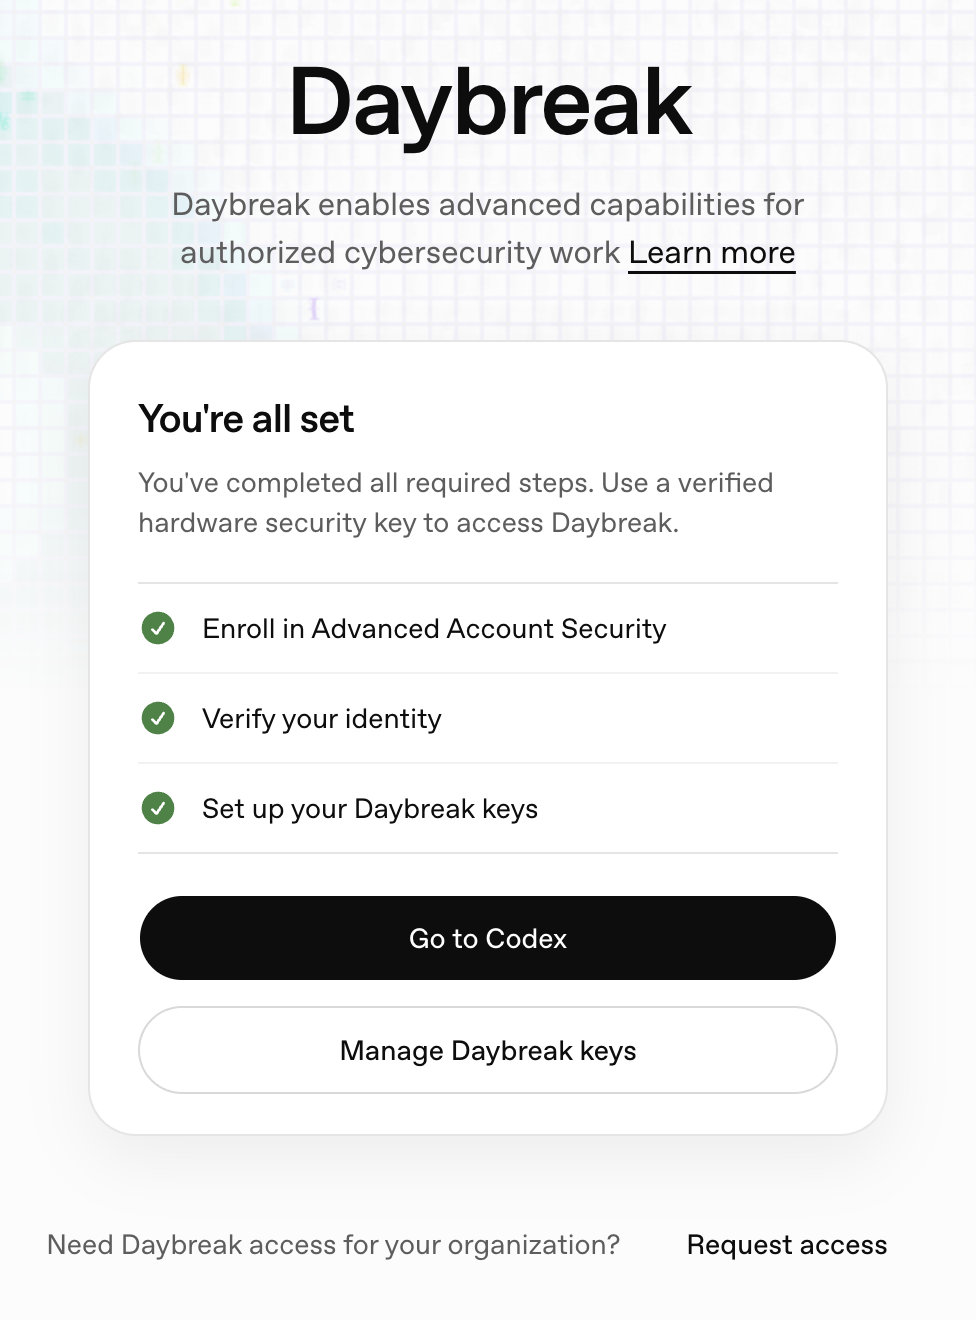
Cropped lossless browser capture from November 9, 2026, after the recorded failures. Codex observed the signed-in ChatGPT profile as Nikolay Kolev before opening this page. No account setting was changed.
Open full-size PNG (976 × 1320; new tab)I described my access as Daybreak Blue. This browser screen confirms completed Daybreak enrollment but does not display a Blue tier label. It also does not reveal which access setting reached the earlier failed requests.
Being told to check a program setting that I already have is frustrating. The interface needs to explain whether the problem is enrollment, a setting that did not reach the request, or a restriction that applies to this task.
What the audit chat actually returned
The chat is titled “Audit dependency CVEs.” Its original request asked for a dependency audit, including the browser bundled with Playwright. The later work included security maintenance for my servers.
The app's chat reader returned six failed turns starting between 12:12:56 and 12:44:51 p.m. Pacific on November 9. All six contain this error:
This content was flagged for possible cybersecurity risk. If this seems wrong, try rephrasing your request. Otherwise, confirm that the access_programs.cyber parameter is set to the appropriate tier, and note that some cybersecurity requests are still limited, even when Daybreak is on.
The distinction matters. The error does not say that my account is outside Daybreak. It explicitly says that limits can remain when Daybreak is on. It also tells me to check an internal-looking parameter without showing whether that parameter was wrong on these requests.
Five of those failed turns followed messages in which I said I was already enrolled and was asking about my own servers. Restating that context did not resolve the failure.
These are failed-turn records. They do not reveal a missing answer or prove that a completed answer was generated and then hidden. The visible result is that the chat failed to deliver an answer.
The problem OpenAI needs to explain
I can show which codebase this is. I can identify the servers I administer. The project history records Codex helping maintain them. I have also reported enrollment in the program named by the error.
Yet the product gives me a generic risk message and no explanation tied to the defensive task. It leaves me unable to tell whether access failed to propagate or whether a separate restriction stopped the request.
The evidence here cannot establish the cause. It does establish a failure that the product should help its user understand and resolve. A useful response would identify the blocked part, show the access status that applied to the request, and explain what permitted maintenance can continue.
I asked for help protecting my own infrastructure. An unexplained block in that workflow deserves a clear answer.
Written by Codex itself
This article was written by ChatGPT Codex itself, at the owner's request. Codex inspected the audit chat's failure records and used Computer Use to capture completed Daybreak enrollment, the private repository, both active servers in the owner's OVHcloud account and the server maintenance history.

 Hacker News
 X
 LinkedIn
Comments
Comments are reviewed before publication. The Author badge marks replies from the author.
Your test session has expired. Stop testing to use comments and sign-in normally, or open a fresh test link to keep testing.
Stopping testing reloads this page in normal mode.
Read approved comments on the discussion page.
Open the discussion page